No more dedicated forensics laptop gathering dust between incidents.
YS::Desktop gives CSIRT and SOC teams a fully isolated investigation workstation on
the device they already use without compromising containment or compliance.
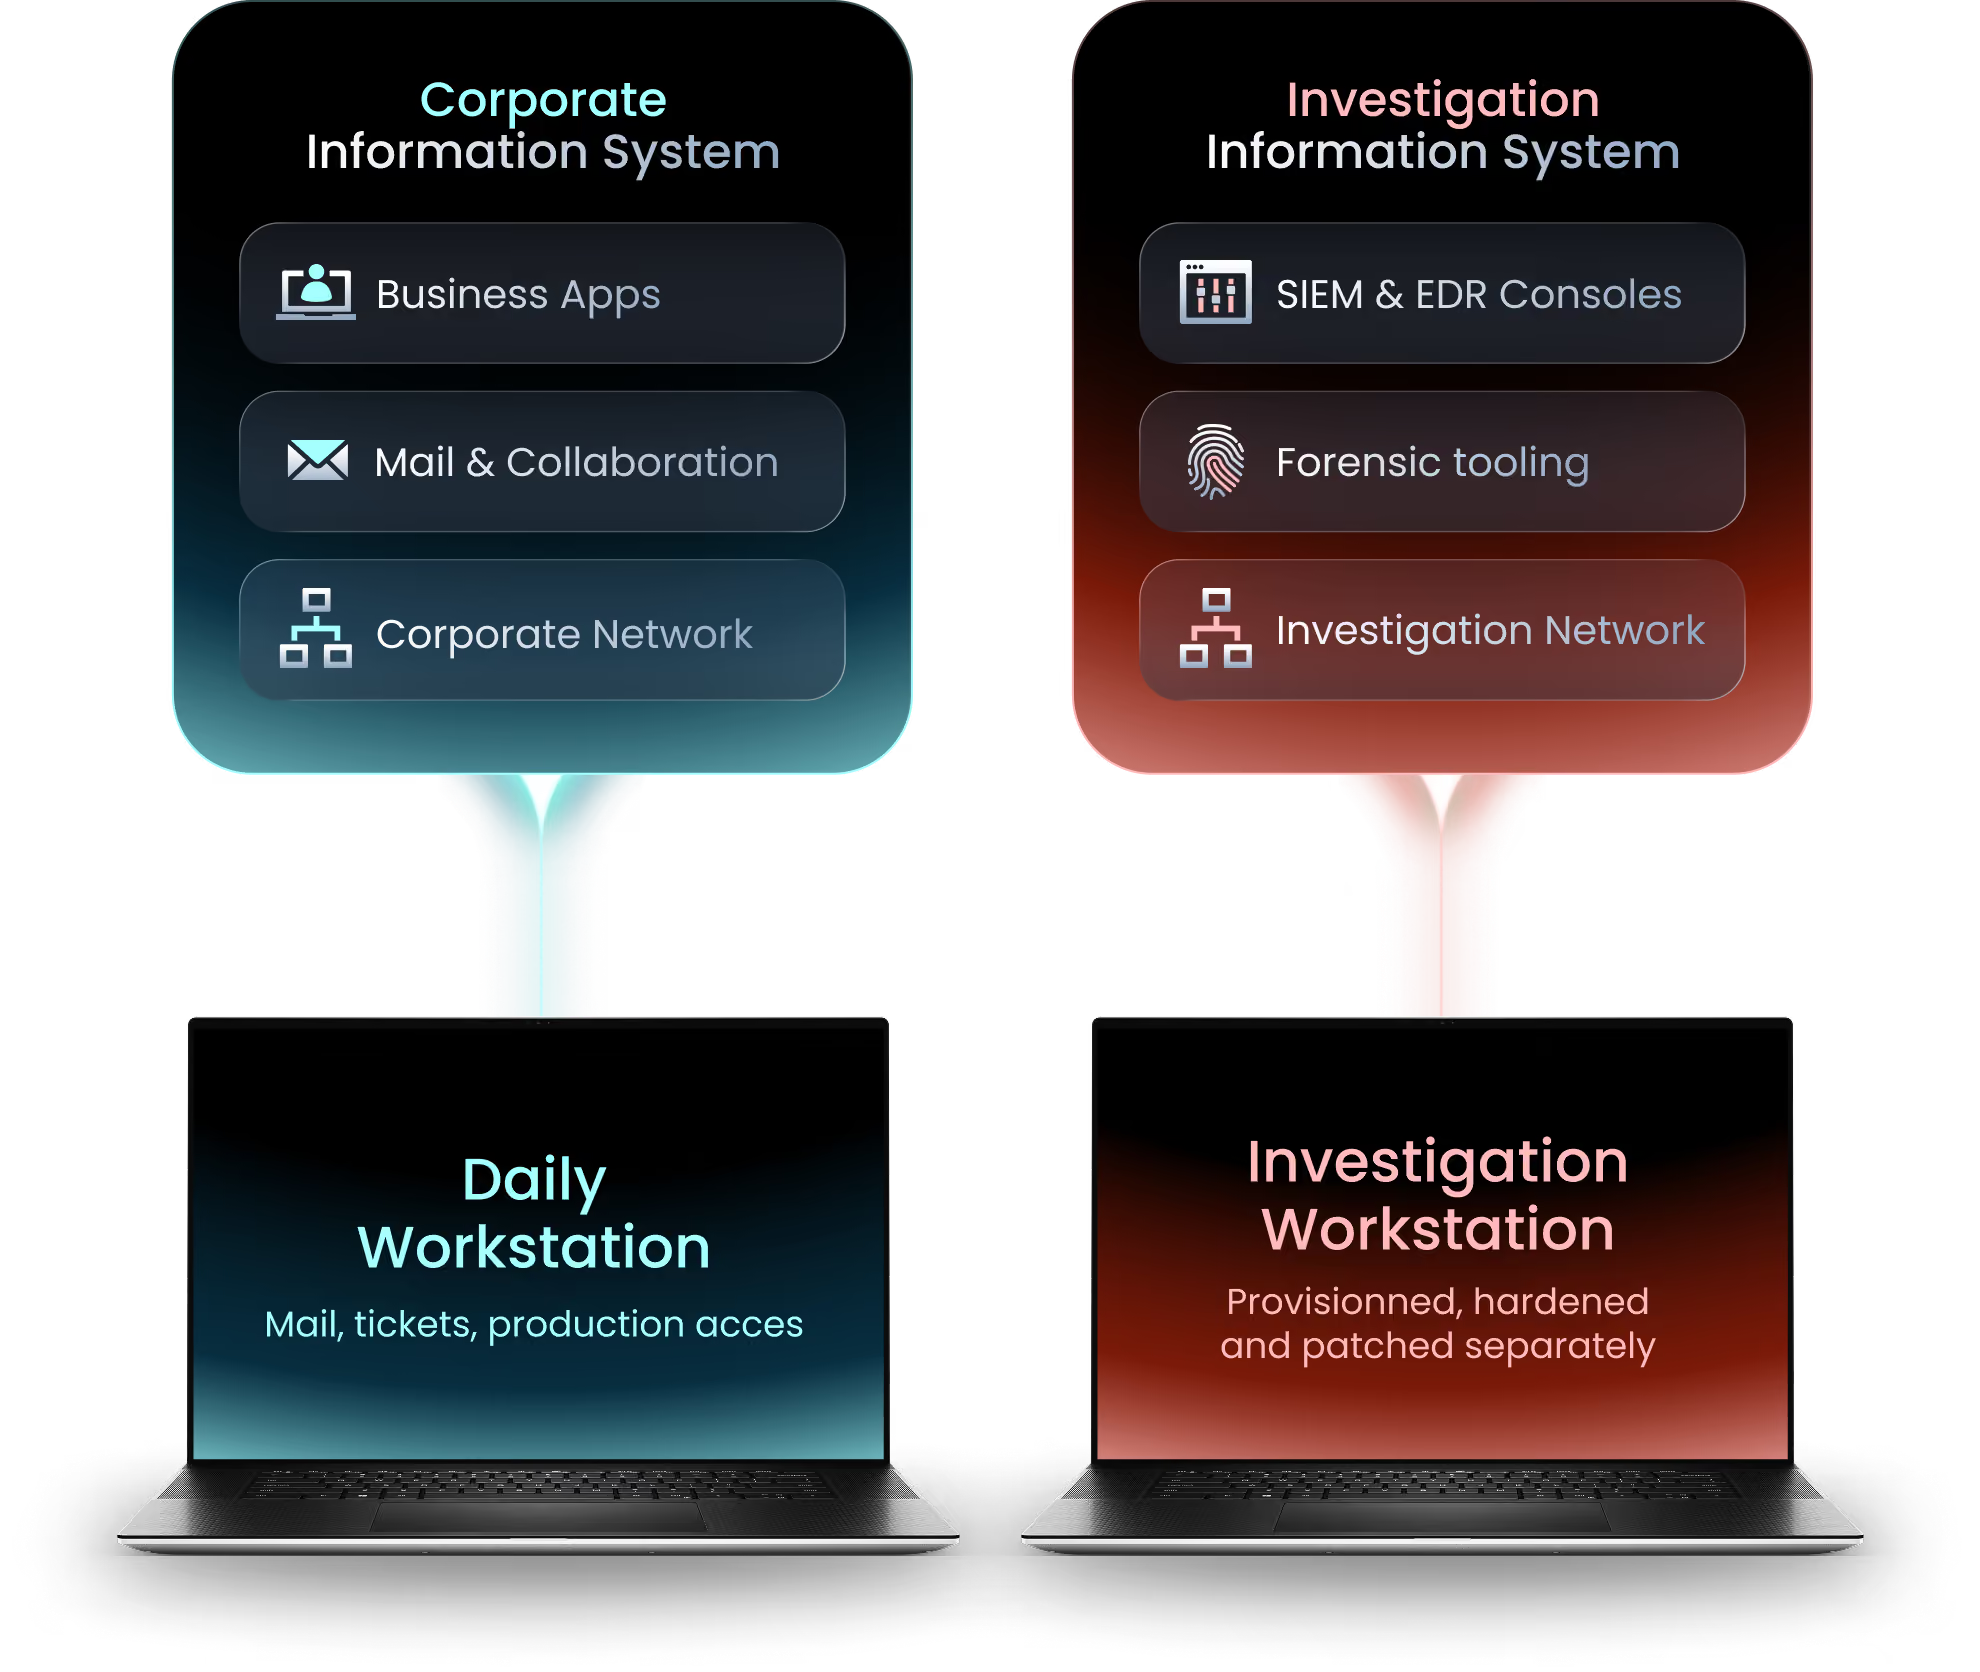
Before
Two devices, distinct network
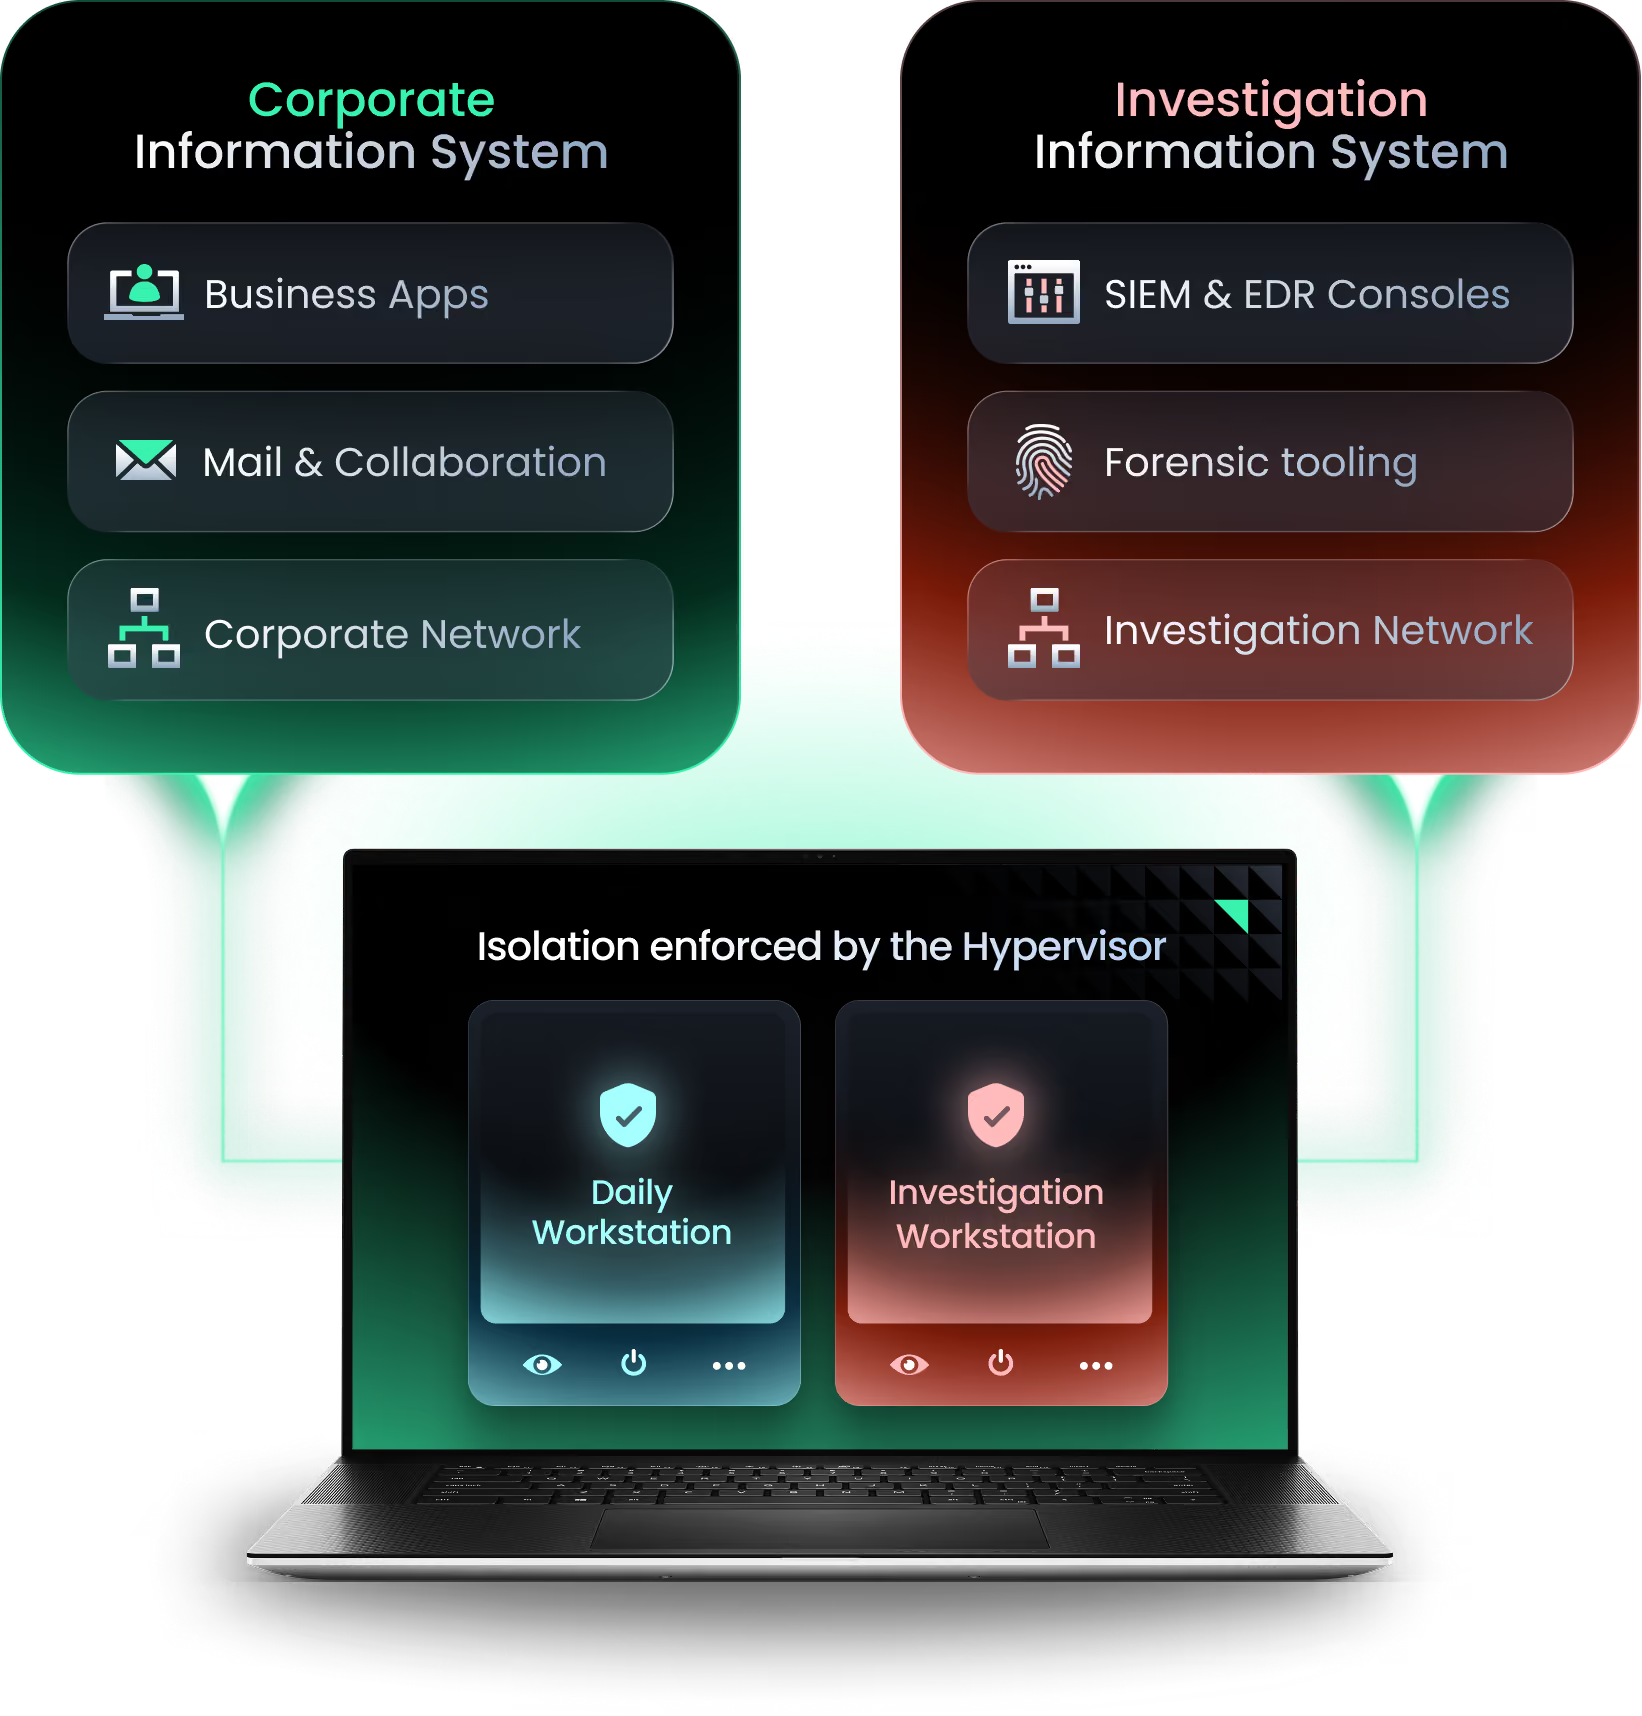
With YS::Desktop
Both coexist, virtualized, on a single device.

Traditional Model :
Dedicated Physical Investigation Workstations
In incident response practice, it's known as a "jump kit": a clean, dedicated forensic laptop, always kept separate from production.
It's standard incident response practice, but it creates real challenges:
Constantly switching between a daily workstation and a separate investigation machine fragments the analyst's workflow, especially under the pressure of an active incident.
Provisioning, hardening, patching, and stocking dedicated investigation workstations, including spares for surge capacity during major incidents, leads to increased cost and complexity.
A fleet of specialized workstations, used intermittently, is harder to keep consistently patched, monitored, and audited.

YS::Desktop: Virtualized, Isolated Investigation Workstation on a Single Device
YS::Desktop replaces these challenges by virtualizing an isolated investigation and remediation environment on the analyst's existing endpoint, contained within its own Security Domain:
No More Switching Devices
The investigation environment runs on the analyst's own workstation, activated in seconds when an incident starts. No more jumping between two machines mid-investigation, no more losing time retrieving a separate laptop while an incident is active.
Isolation Without the Fleet
Each investigation environment runs inside its own Security Domain, isolated by the hypervisor itself. No sample can reach production or the daily workstation, without needing a physically separate machine to guarantee it, and without a dedicated fleet to provision, harden, and patch.
Instant Clean Reset
Save an investigation environment in its clean, pre-incident state and roll it back once remediation is complete. No wiping and reinstalling the OS and every tool between two incidents, and no spare machines to keep stocked for surge capacity.
A Dedicated Audit Channel
Every investigation domain forwards its activity over a dedicated monitoring channel to the Audit service, ready to feed your existing SIEM/SOC stack. One consistent audit trail, instead of a fleet of intermittently used machines that's harder to keep monitored.

The Benefits : Respond Faster, Spend Less, Stay Compliant
No time lost retrieving a separate machine or waiting for a spare to be provisioned. The investigation environment is ready the moment an analyst needs it, so the response clock starts sooner — not after logistics are sorted out.
No dedicated fleet to provision, harden, patch, and keep in reserve for surge capacity. The cost of staying ready for the next incident drops to what it takes to activate a Security Domain, not to maintain a parallel set of machines most of the time sitting idle.
Meet isolation requirements from NIS2, ISO/IEC 27035, and sector frameworks — without a separate audited fleet to prove it.
“ We’ve been waiting for a solution like yours for 15 years ”

Questions analysts will ask
before choosing a solution
Ready to isolate
Without Compromise?
Live walkthrough by specialists who've solved this for teams like yours.