

Active Directory Tiering: Which Assets Are Really Tier 0?




Tiering principles are a bit like grammar rules. At first, everything seems simple: you learn a few rules, apply them, and everything seems to fall neatly into place.
Tier 1 covers servers and business applications. Tier 2 covers workstations and users. As for Tier 0, most people remember it as the domain controllers.
But, just as with grammar, this first reading doesn’t capture the whole picture.
In most tiering projects, the truly critical scope extends far beyond what is actually protected. Tier 0 isn’t limited to domain controllers. Many components hold, directly or indirectly, enough privilege to compromise the entire environment.
Yet the strength of the model rests on one essential question: what really belongs in Tier 0?
Which assets should be treated as Tier 0?
Tier 0 includes every asset capable of taking control of Active Directory, directly or indirectly. That obviously includes domain controllers, but also any system that can reach their secrets or run code on them.
Domain controllers are only the tip of the iceberg. Many systems hold enough privilege or control to compromise the directory, sometimes without ever connecting to it directly.
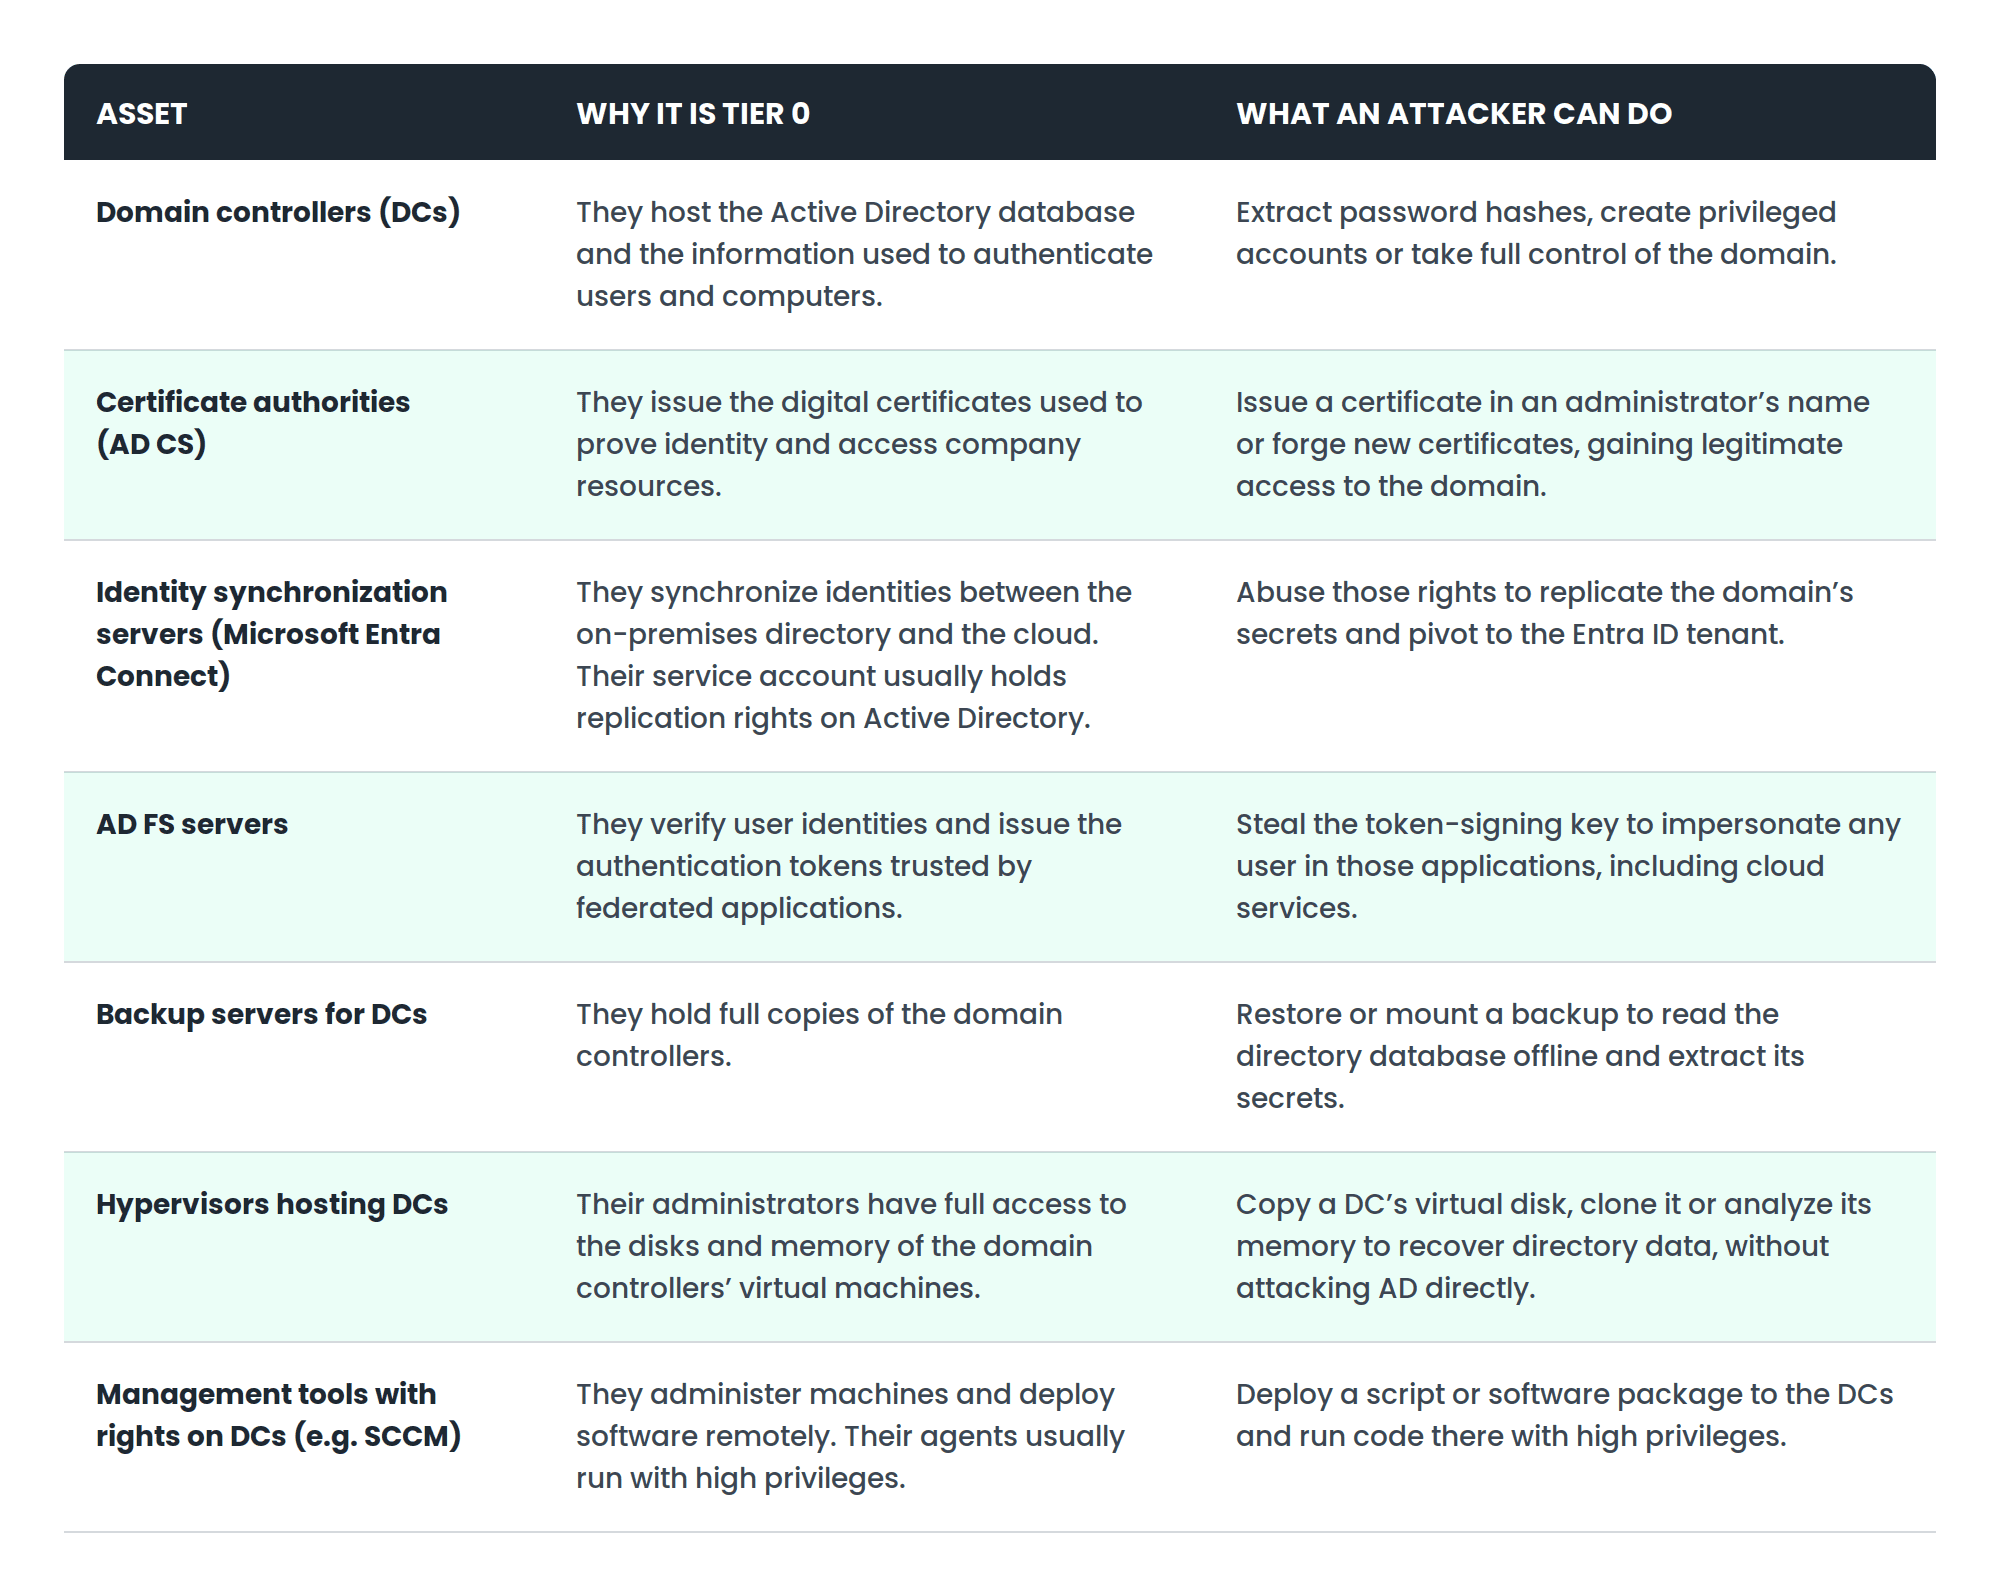
Compromising just one of these assets amounts to controlling the domain, or the access it protects. Tier 0 can’t be defended like a perimeter: it is only as secure as its weakest link.
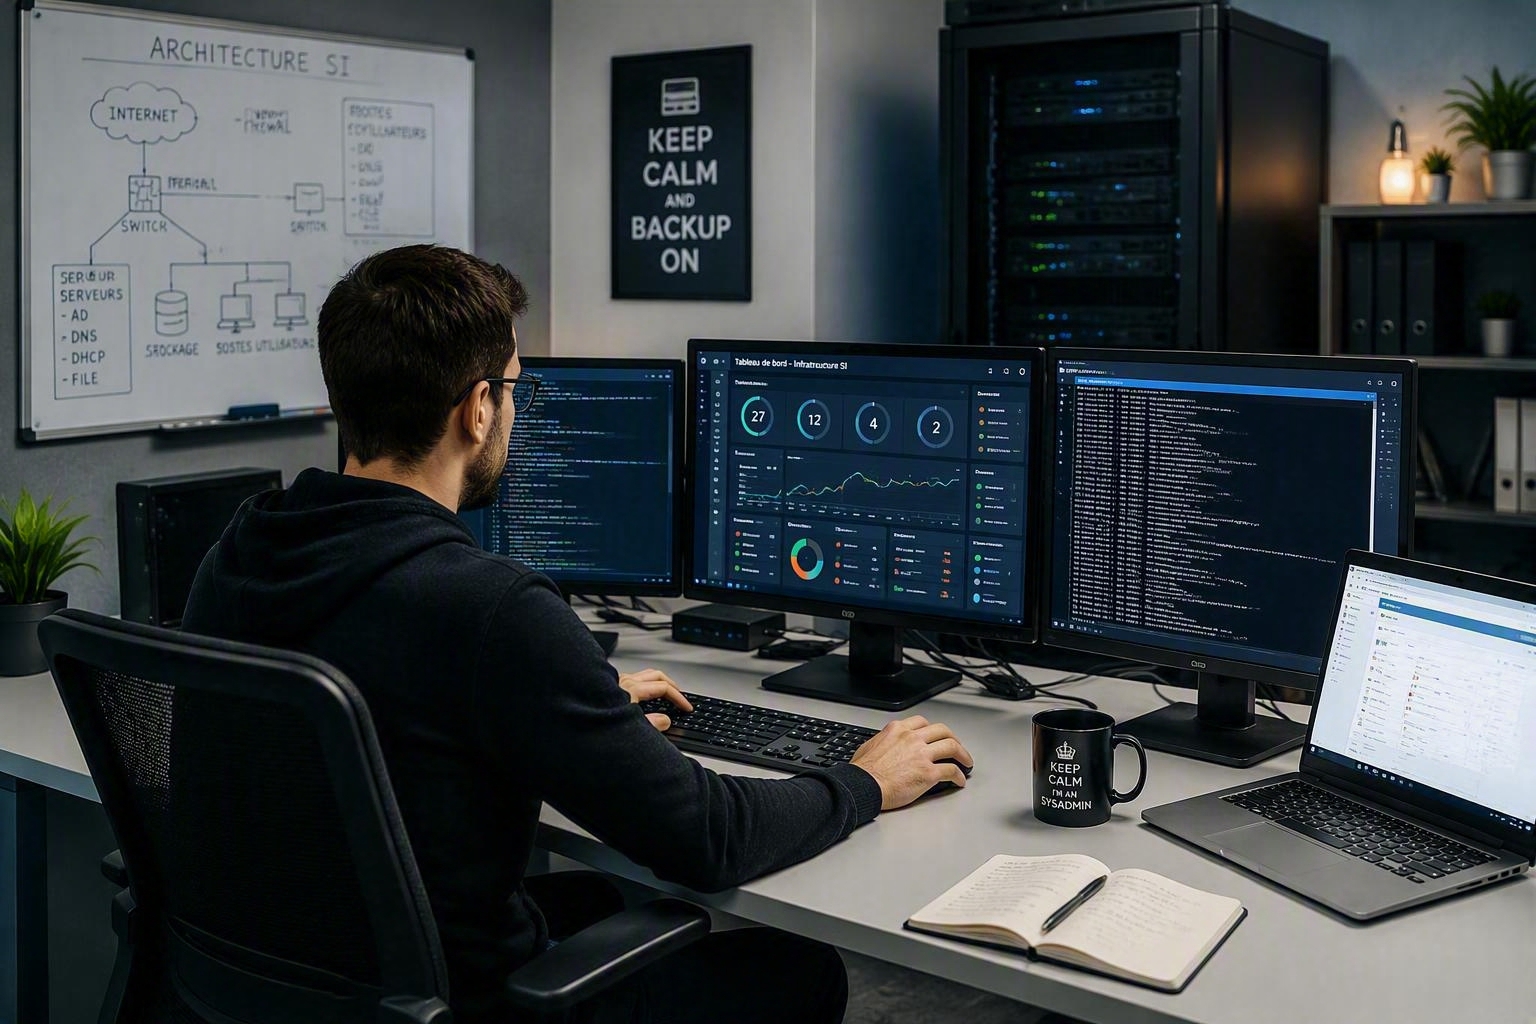
Here’s an example. Imagine that Marc, an administrator at your company, uses his everyday office PC to manage the domain controller through a hypervisor. The problem here isn’t the hypervisor, it’s the workstation Marc is using. Why? Because his office PC, unlike an administration workstation, belongs to Tier 2. It’s like hiding the company safe in the meeting room.
If someone manages to compromise Marc’s PC one day, they can then compromise the hypervisor, and then the domain controller. No bueno.
They won’t even bother attacking the controller. All they need to do is copy the virtual machine, mount its disk on another system and analyze the directory and its data offline.
Put another way: if a thief can get into the meeting room, they won’t waste time cracking the safe in front of the cameras. They’ll carry it off and open it quietly somewhere else.
The same reasoning applies to a certificate authority, a backup server or an SCCM server. Each one is an indirect path to the domain’s secrets.
And once those secrets are in hand, an attacker can stay in place for a long time, even after passwords are changed, for example with a forged Kerberos ticket (as long as the krbtgt account password hasn’t been reset twice) or a fraudulent certificate.
This is why ANSSI, the French national cybersecurity agency, recommends treating these assets as a single, consistent whole, administered from dedicated resources.
Control paths to secure when rolling out tiering
When deploying tiering, one common trap is to focus on the hypervisor and forget to bring its management console, its storage array, or the iDRAC and iLO interfaces of the physical servers hosting the DCs into Tier 0.
On top of the virtualization chain come the agents installed on domain controllers. An EDR, a monitoring tool or a patch management platform effectively extends the Tier 0 scope to its administration console. The same goes for tools that protect or store Tier 0 secrets: they become Tier 0 themselves.
The risk of compromise doesn’t only come from outside AD; it can also come from within. A poorly protected GPO applied to domain controllers can be enough to take control of them and run code there. Then there are built-in groups such as Backup Operators, Server Operators or Account Operators, which sometimes hold privileges that have been forgotten for years.
Finally, delegations granted at the domain root or on sensitive objects can open control paths to Tier 0 without anyone noticing.
For an attacker, these are all paths leading to the domain controllers. To avoid missing any, the simplest approach is to start from the domain controllers and trace every control path back: who can act on this asset, and who can act on those? Active Directory attack path analysis tools help make these dependencies visible.
The workstation: the last link in the chain
It may well be the most overlooked asset in tiering projects. Yet in many attack scenarios, the compromise doesn’t go through the server itself, but through the workstation used to administer it. If, like Marc, the administrator uses his office PC, he opens a control path for the attacker. The model collapses.
This is why ANSSI’s security recommendations call for separating administration environments from everyday office use. Its guide on secure administration describes several options: a workstation dedicated exclusively to administration, or a multi-level administration workstation that isolates environments on a single machine.
The dedicated workstation is a logical answer, simple on paper but restrictive day to day. Restrictive enough to drive behavior like Marc’s, who administers sensitive resources, reads his emails and sometimes watches cat videos, all on the same PC.
When securing Tier 0 admin workstations, the challenge isn’t so much isolating the administration environment as doing it without degrading the administrators’ experience.
Conclusion: protecting the workstations that administer Tier 0
Physical separation, while effective, often means buying additional workstations, putting more constraints on administrators and, ultimately, a lot of workarounds. A situation that rarely satisfies anyone.
At Kerys, we offer a different approach to this dilemma. Our Type 1 hypervisor, YS::Desktop, isolates and runs multiple environments on a single physical PC. On the same workstation, a Tier 0 administrator has one environment dedicated to Tier 0 and another for checking email. With a single swipe, they switch from one to the other while keeping the two strongly separated. YS::Desktop meets the technical criteria for multi-environment workstations set out in ANSSI guide PA-114.
You might also be interested



Ready to isolate
Without Compromise?
Live walkthrough by specialists who've solved this for teams like yours.